Identity & tenant boundaries
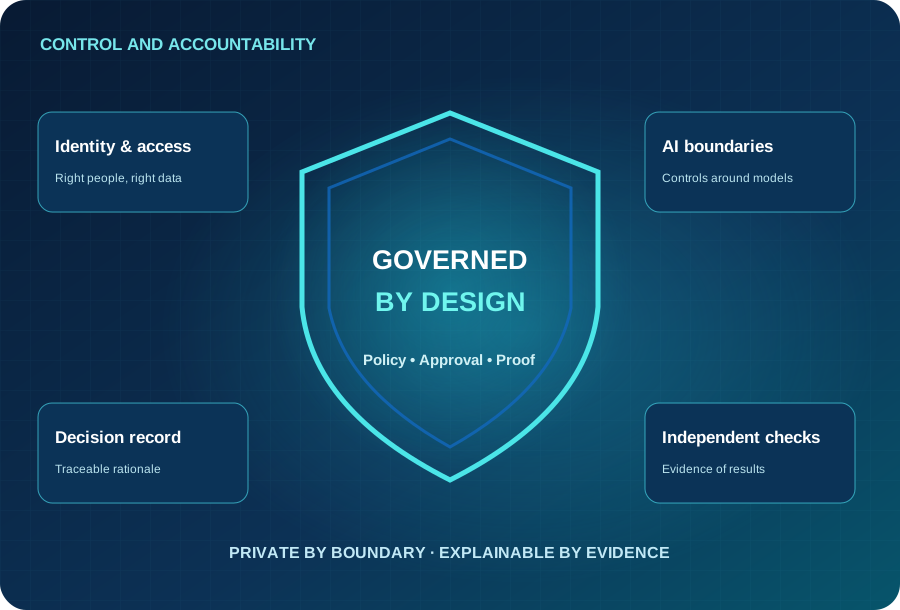
Role-based access, least privilege and organization-specific data boundaries govern what users, services and delegated administrators may see and do.
SECURITY & ACCOUNTABILITY
Enterprise intelligence should make complex work more understandable without weakening privacy, authority or accountability. Ceryvra is being designed to preserve those boundaries from first connection to final verification.
An AI suggestion, a human approval, a completed action and a verified result are distinct events—and the platform is intended to treat them that way.
CONTROL IS PART OF THE PRODUCT
These are architectural design requirements. Deployment-specific controls and production effectiveness must be demonstrated through integration and security acceptance testing.
Role-based access, least privilege and organization-specific data boundaries govern what users, services and delegated administrators may see and do.
Recommendations never grant themselves permission. The Core evaluates current policy, evidence and delegated approvals before permitted action.
Versioned sources, rationale, decisions, actions and exceptions preserve a defensible history without confusing generated content with established evidence.
A successful API response does not equal a successful business outcome. Verification checks observed conditions and keeps incomplete or failed cases open.
DESIGNED FOR RESPONSIBLE INTELLIGENCE
High-stakes recommendations require appropriate review. Cross-organization learning is not enabled without an approved privacy architecture. When an outcome is unknown, the workflow should reconcile or recover rather than assume success.